Executive Summary: The $25,000 Blindspot
- The Threat Landscape: High-producing advisors selling luxury FITs and long-haul business class flights are prime targets for international fraud rings using compromised card data.
- The Chargeback Trap: Banks side with cardholders by default. Without 3D Secure verification or legally compliant digital authorization forms, advisors lose 82% of card-not-present (CNP) disputes.
- Merchant of Record (MOR) Shield: Booking directly through suppliers (wholesalers, cruise lines) protects advisors from payment liability. Acting as MOR on planning fees or direct ticketing requires specialized chargeback defense protocols.
- The Zero-Loss Protocol: Vincent Vacations provides top-tier fraud screening frameworks, digital client authorization templates, and turnkey dispute dossiers to safeguard host members.
 Modern travel agencies must treat transaction security and identity verification as core operational disciplines.
1. The Financial Peril: How a Single Chargeback Destroys Quarterly Profit
For independent travel advisors generating $1,000,000 to $5,000,000 in gross annual sales, gross revenue can obscure thin cash margins. On a complex $35,000 luxury safari or multi-cabin Mediterranean cruise booking, an advisor’s net commission might represent $4,500 to $5,600.
However, if that booking is executed with a compromised credit card or a bad-faith traveler who initiates a fraudulent chargeback claiming “Services Not Received” or “Fraudulent Card Use,” the financial liability does not merely wipe out the commission. Under traditional card merchant agreements and poorly structured host contracts, the entire $35,000 transaction amount is clawed back immediately from the agency’s operating account, alongside penalty fees and potential merchant account termination.
A single unresolved chargeback of this magnitude can erase the net profits of twenty successful bookings. In this masterclass, we dissect how predatory fraud syndicates operate in the travel industry and provide the exact defense mechanisms top producers use to protect their revenue.
2. The 7 Red Flags of Travel Fraud: Spotting Bad Actors Early
Professional fraudsters rarely target low-cost domestic travel. They specifically seek out high-producing, bespoke advisors because luxury bookings allow for rapid liquidation of high-value services before cardholder discovery.
Every advisor on your team must be trained to recognize the 7 Core Red Flags before running a transaction:
1 High-Value, Last-Minute International Departures
Inquiries requesting business or first-class international airfare or luxury resort suites departing within 48 to 72 hours. Fraudsters operate under extreme time pressure to consume travel before the legitimate cardholder reviews their online banking statement.
2 Complete Price Insensitivity
Legitimate luxury clients are wealthy, but they are astute consumers who care deeply about value, amenities, and room tiers. A client who approves a $20,000 quote instantly without inquiring about cancellation terms, flight connections, or room upgrades is a major red flag.
3 Name Discrepancies Between Cardholder & Passenger
The cardholder name does not match any traveler on the booking manifest, and the caller offers vague explanations (“booking for my executive assistant’s cousin”). Never process third-party credit cards without explicit, notarized corporate authorization.
4 Resistance to Video Consultations or Phone Calls
The client refuses to hop on a 10-minute Zoom consultation, insists on communicating strictly via encrypted messaging apps or burner email domains, and refuses to provide a verifiable LinkedIn or company profile.
5 Split Payments Across Multiple Unrelated Credit Cards
When the first card declines, the prospect immediately supplies two or three other cards under completely different names or cardholder zip codes. Fraud syndicates test multiple stolen credit card numbers until one clears.
6 Urgent Requests for Cash Refunds or Alternate Payouts
The traveler overpays or cancels abruptly and demands that refund proceeds be wired via Zelle, Venmo, Western Union, or a different bank account “due to a banking emergency.” This is the classic money laundering chargeback double-dip.
7 Geographically Incoherent IP & Billing Data
The client claims to reside in Manhattan, but their email header IP originates from West Africa or Eastern Europe, and the card billing address belongs to an empty commercial lot in Florida.
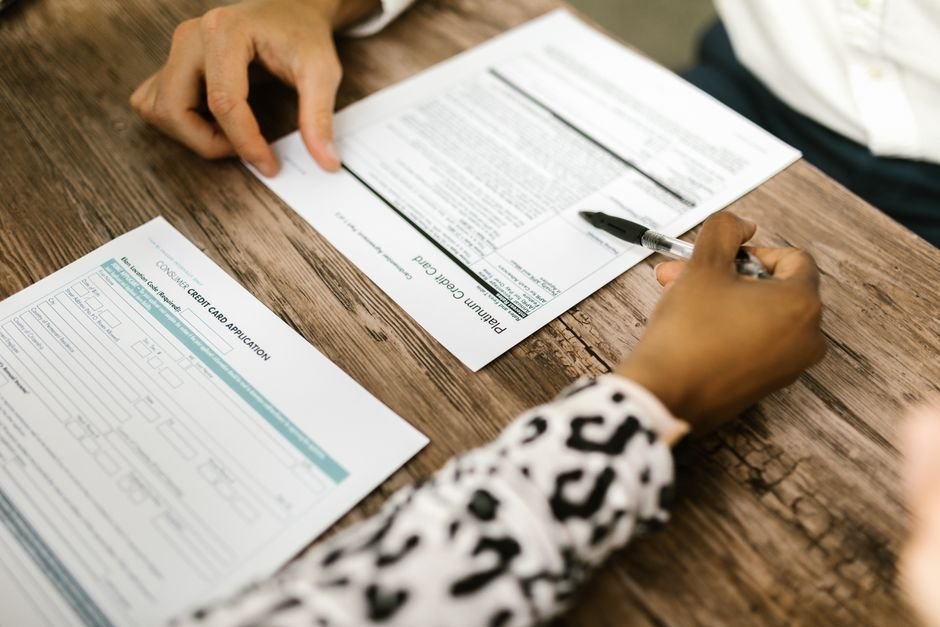 Written credit card authorizations with clear cancellation terms are your primary legal defense in cardholder disputes.
3. Merchant of Record (MOR) Demystified: Supplier Direct vs. Agency Processing
Understanding your position in the transaction flow is essential for managing liability. In travel distribution, there are two distinct payment architectures:
| Transaction Model |
How It Works |
Who Holds Chargeback Liability |
Advisor Risk Level |
| Supplier-Direct (Pass-Through) |
The advisor takes client card details and submits them directly into the supplier engine (e.g. Classic Vacations, Regent Seven Seas, Tauck). The supplier descriptor appears on the client statement. |
The Supplier / Wholesaler holds primary merchant liability. If the client disputes, the supplier manages arbitration. |
Low Risk (Commission may be recalled if canceled, but no net capital loss). |
| Agency as Merchant of Record (MOR) |
The advisor charges the client via their own Stripe, Square, or host merchant account (e.g. for non-refundable planning fees, custom group deposits, or net air ticketing). |
The Advisor / Agency. Card brand networks pull 100% of disputed funds directly from your bank account during investigation. |
High Risk (Requires strict 3DS protocols and written contracts). |
Best Practice Rule: Whenever booking leisure travel packages, always utilize supplier-direct pass-through processing. Only act as Merchant of Record for your own professional travel design fees, and ensure your fee contract explicitly states that fees are non-refundable for professional consulting services delivered immediately upon engagement.
4. The Enforceable Credit Card Authorization SOP & Digital Signatures
Never process a payment based on an unverified email or text message saying “Go ahead and charge my Amex.” In credit card arbitration, text messages and standard emails carry zero legal evidentiary weight.
Your agency must enforce a mandatory Standard Operating Procedure for Payment Authorization:
Mandatory Credit Card Authorization Clauses
Every authorization must capture: (1) Cardholder Full Legal Name, (2) Billing Address & Zip Code, (3) Last 4 Digits of Card & Expiration, (4) Specific Dollar Amount Authorized, (5) Itemized Description of Travel Services, (6) Explicit Supplier Name Appearing on Statement, (7) Non-Refundable Planning Fee Acknowledgement, (8) “Cardholder agrees not to initiate a chargeback for travel disruptions, weather cancellations, or supplier bankruptcy, and agrees that all claims shall be pursued under travel insurance or directly with the service provider.”
Digital signature platforms such as DocuSign, PandaDoc, or Travefy Payment Authorizations capture timestamped IP addresses, browser user-agents, and cryptographic signature hashes. This digital audit trail is the single most important document required by Visa and Mastercard dispute arbitration panels.
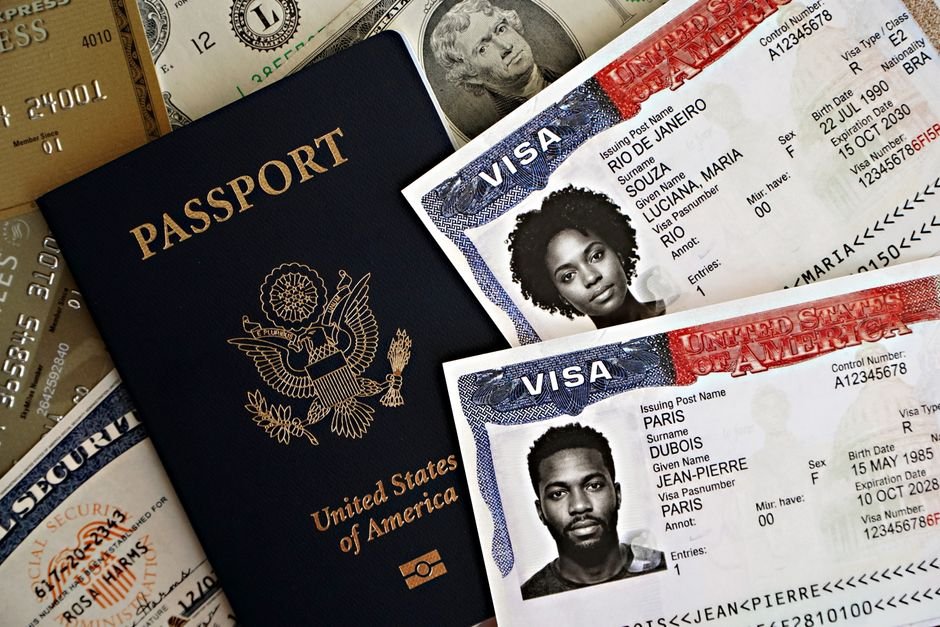 Verifying government-issued identification against billing records eliminates 99% of identity theft transactions.
5. 3D Secure (3DS) & EMV Mandates: Why Email Confirmations Fail in Arbitration
Under Visa and Mastercard operating regulations, the burden of proof in Card-Not-Present (CNP) transactions rests entirely on the merchant. If a consumer files Reason Code 10.4 (Other Fraud – Card-Absent Environment), the issuer will reverse the charge unless the merchant can prove that 3D Secure (3DS) authentication occurred.
3D Secure (often branded as Verified by Visa, Mastercard Identity Check, or Amex SafeKey) passes a two-factor authentication challenge directly to the cardholder’s mobile banking app or SMS. When a transaction completes via 3DS, liability shifts from the merchant to the issuing bank. Even if the cardholder later claims they never authorized the purchase, the bank cannot claw back the funds from the merchant.
If your host agency or payment gateway does not support 3DS2 authentication for client payments, your agency is needlessly exposed to total liability on every single booking.
6. The Chargeback Rebuttal Dossier: Compiling Winning Evidence for Card Issuers
When a chargeback notification arrives, the merchant typically has only 10 to 14 calendar days to submit a comprehensive rebuttal packet. Submitting a hasty email stating “the client booked this vacation and enjoyed it” results in an immediate loss.
A winning Chargeback Rebuttal Dossier must be organized logically with numbered exhibits:
- Exhibit A: Executive Cover Letter: A concise 1-page chronological narrative summarizing the client relationship, booking timeline, and specific rebuttal of the cardholder’s claim.
- Exhibit B: Signed Credit Card Authorization: The legally binding, timestamped digital authorization document showing IP verification and matching billing address.
- Exhibit C: Itemized Supplier Invoices & Itineraries: Confirmation vouchers displaying the cardholder and traveling passengers’ names matching the itinerary.
- Exhibit D: Proof of Service Delivery: Hotel check-in logs, airline boarding passes, or cruise embarkation manifests confirming that travel was completed without dispute.
- Exhibit E: Client Communication History: Written WhatsApp, SMS, or email exchanges where the client thanked the advisor for their trip or confirmed receipt of travel documents.
- Exhibit F: Signed Terms & Conditions and Insurance Waiver: Proof that the client agreed to non-refundable cancellation terms and acknowledged their travel insurance options.
7. Client PII Protection & Agency Cybersecurity Standards
Travel advisors are custodians of the most sensitive personal identifiable information (PII) imaginable: full legal names, dates of birth, passport scans, credit card numbers, home addresses, and travel schedules.
If an advisor’s email account is compromised, cybercriminals can monitor communication threads, intercept supplier payment links, or pose as the advisor to request wire transfers from wealthy clients.
Vincent Vacations Cybersecurity Protocols
To maintain executive agency standards: (1) Mandate Multi-Factor Authentication (MFA) across all email and CRM platforms, (2) Never store raw credit card CVVs or full numbers in spreadsheets or unencrypted notes, (3) Use secure client intake portals such as VacationCRM with end-to-end tokenization, and (4) Maintain an active Cyber Liability & Data Breach Insurance policy alongside traditional E&O coverage.
Executive Partnership
Protect Your Book of Business with Vincent Vacations
Looking for a host agency that provides institutional-grade merchant security, VacationCRM compliance tools, top-tier E&O coverage, and up to 100% commission splits? Discover our Zero-Loss Host Transition Protocol.